How a Studio Earns the Right to Touch Your Freelancer-Built Codebase
A good studio audits first and rewrites only when the evidence demands it.
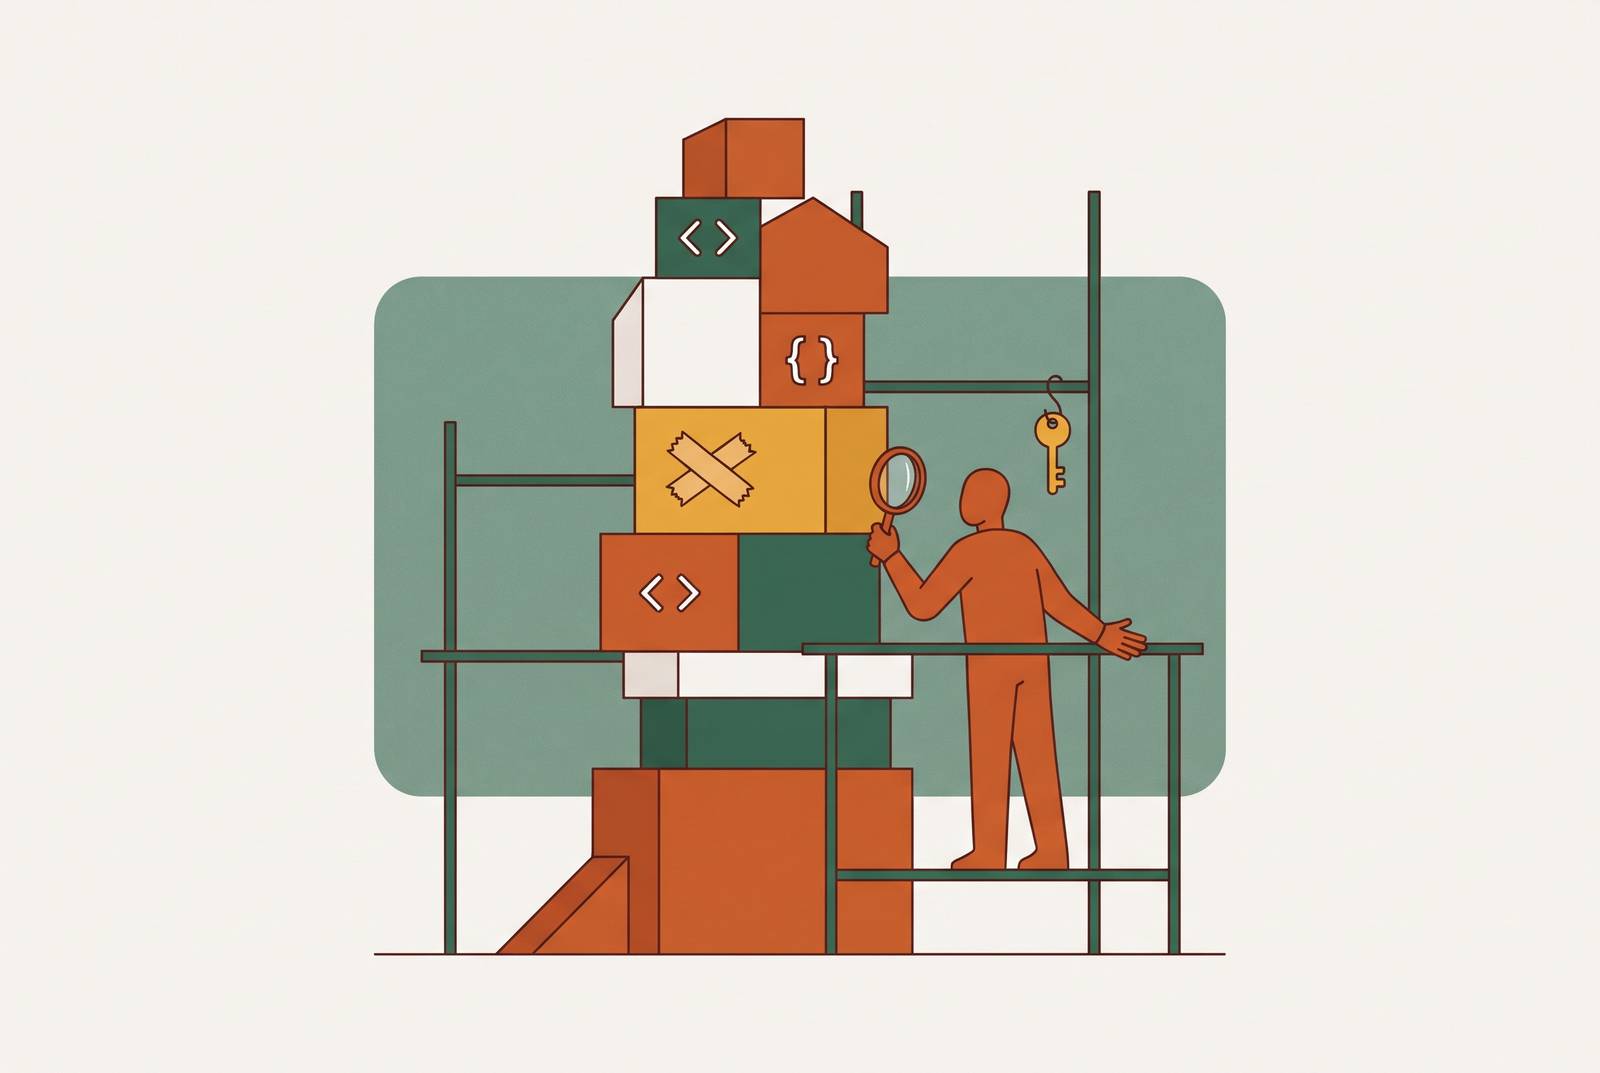
For a post-MVP rebuild of an AI-generated or freelancer-built codebase, hire a studio that audits before it proposes a rewrite. It should establish ownership, document risks, and agree with the founder on what to preserve, refactor, or replace. The right to touch the product is earned through that process.
Why freelancer-built codebases carry a specific kind of structural debt
Freelance engagements often ask people to finish a task, leaving care of the system over the long term outside the job. That distinction shapes what gets built. A contributor can deliver the requested feature without being responsible for how it fits with features added later. When successive contributors bring different libraries, patterns, and conventions, each piece may work while the architecture fragments at the seams. Without enforced governance, local decisions become a structural problem.
The missing element is continuity of ownership. When the person who built a critical module leaves, their understanding of its trade-offs and failure modes leaves too. Documentation helps, but it rarely substitutes for working knowledge of the code. The next contributor inherits the implementation without necessarily inheriting the reasoning behind it. Over time, that gap makes changes harder to judge.
The engagement is mismatched with the software’s needs. A task can end when its acceptance criteria are met, while a production system needs someone responsible for what happens afterward. A studio taking over must understand that distinction, because changing the contributors while keeping the same ownership model leaves the same weakness in place.
What actually breaks when this codebase meets real users
The production threshold exposes weaknesses that an MVP can leave hidden. The product now has to do more than demonstrate an idea. N+1 database queries, serverless cold starts on hot paths, database connection exhaustion, and un-code-split frontends are concrete failure modes an audit should investigate. AI features can also lead to model-cost blowouts. These are different problems, so a general claim that the application “does not scale” is not a sufficient diagnosis.
What, exactly, is failing under real use? That question separates an engineering assessment from a sales pitch. A database problem does not, by itself, establish that the frontend needs replacing. Nor does an expensive AI feature prove that the whole application is unsalvageable. The founder needs a vocabulary precise enough to connect each proposed change to a specific risk.
Security belongs in that assessment as well. Wiz’s report on MoltBook described an exposed production database containing API authentication tokens, email addresses, and private messages between agents. It also identified plaintext OpenAI API keys inside those messages. The case illustrates the stakes of production exposure, without establishing that every inherited MVP has the same defects. For a founder, those stakes include not only service reliability and user trust but also the cost of finding and correcting what the first build left unresolved.
The cost a founder is actually carrying before a studio arrives
Technical debt consumes resources before anyone signs a takeover agreement. McKinsey research identifies it as a significant drain on IT budgets, diverting spending from value-creating work. Developer time spent dealing with existing weaknesses cannot also go toward growth. The burden therefore includes more than the cost of future repairs. It includes the work the organization cannot pursue while upkeep absorbs its capacity.
Resource-constrained organizations have less room to absorb that burden. A nonprofit can find much of a limited IT budget going toward operational upkeep, leaving less for programmatic impact. Where documentation is thin, turnover also interrupts momentum and can send staff back to spreadsheets. The product may still be available while the organization grows less sure that it can use or change it. That is a cost even when it does not appear as a separate invoice.
Yet technical debt can be a valid strategy. For a first build, it may make sense to get a product into use before dealing with every long-term concern. A responsible studio makes that trade-off visible. Its engagement should relieve an existing burden while respecting the work the founder has already funded.
Why the right to touch this codebase must be earned, not assumed
The codebase represents more than its current technical condition. It contains work already paid for, decisions made under constraints, and a product on which users have placed their trust. A studio that calls it a mess before examining it dismisses that investment. Technical confidence does not excuse that dismissal. Respect begins with understanding why the system exists in its present form.
ReflektLab’s takeover methodology distinguishes taking responsibility for an existing application from replacing it. Its approach starts with what already exists and works, proposing component replacement only when that component justifies it. The justification comes before work begins. That distinction protects the founder from discovering that an apparent takeover has become a rewrite, discarding paid-for work and pushing the next release months out.
Reputation cannot substitute for this discipline. A studio earns legitimacy by making invisible debt visible and allowing the founder to participate in the decision about it. Offering a rewrite package before seeing the code reverses that order, putting the proposal ahead of the diagnosis. It is both technically reckless and a failure of trust. More fundamentally, it repeats the task-based model by treating the product as a new scope to sell when it should assume responsibility for the existing product.
How should a studio assess whether to refactor or rewrite before writing a single line?
A founder should expect to be asked who owns the code before engineering begins. AW3’s codebase takeover journal places IP clarity first, because a team cannot legally take over sources it has no right to modify. Accounts must move into the client’s name, secrets must be rotated, and IP must be assigned in writing before the audit starts. These requirements establish whether the proposed work can properly proceed at all.
The audit then needs a defined scope and price. Leanware’s code audit service provides a concrete model, with one senior engineer assessing security, architecture, tests, deployment, and monitoring over one to two weeks for a fixed fee. Its deliverables include a prioritized fix list and a quote to certify and take over the application. The founder is buying an assessment before committing to a larger engagement. That gives the studio responsibility for a bounded deliverable rather than an open-ended opportunity to discover more work.
Written findings must precede remediation, and the founder must help decide what follows. Which defects need attention first, which components can remain, and what evidence supports replacement? Those questions should be answerable from the assessment. A narrow audit is also not the same as a complete takeover. Most takeovers take 2–4 weeks for initial assessment and 1–4 months for full stabilization, so promises of a faster outcome before anyone has seen the code deserve skepticism.
Red flags in a studio’s approach that reveal the wrong values
A polished portfolio does not make up for offering a rewrite package before looking at the code. Condemning earlier work without looking at it is another warning sign, because the studio has decided what to sell before it knows what shape the code is in. In both cases, the studio has chosen its answer too early. The studio puts the work it wants to sell ahead of what the founder needs.
Without a written, prioritized defect list, the founder cannot clearly connect the audit to the proposed work. Skipping the IP conversation leaves a more basic question unanswered, namely whether the team has the right to proceed. A handoff-and-disappear contract presents another risk even if the immediate repair is sound. It leaves no long-term owner of the codebase’s health.
A studio should be explicit about what it will not change and why, rather than treating every untouched component as unfinished business. Component-level justification also gives the founder something concrete to evaluate. The distinction is between a team that seeks permission for an informed plan and one that treats access as permission to decide alone.
When the data layer is also freelancer-built: the Airtable question
A studio needs to look as closely at Airtable as it does at application code. Its accessibility without engineering staff makes it useful to nonprofit and mission-driven teams, but it can become a bottleneck as operations grow. A studio first needs to understand what the team built and why it wants to leave. Cost, record limits, permissions, and outgrowing the grid point toward different choices.
If cost is the reason, the evaluation concerns whether another platform can preserve the useful shape of the existing system. Baserow, NocoDB, and Teable are self-hostable alternatives worth considering in that context. Licensing needs care, however. Baserow and Teable are open source, while NocoDB’s master branch moved to the Sustainable Use License in January 2026 and is source-available.
If record limits are the constraint, those alternatives or a real database warrant evaluation. NocoDB is particularly relevant to a team already running a database because it wraps a GUI around the existing data layer and preserves it. Supabase provides a Postgres database, authentication, file storage, generated APIs, and row-level security. That makes it a candidate when the application needs a production backend. Neither option answers the question until the audit establishes what the current data layer must support.
Where the required permissions cannot be expressed in Airtable, a custom build becomes the relevant path to assess. Jet Admin provides team-based permissions, activity logs, and data blending across database types for engineering-heavy or IT-led teams building business apps on existing data sources. If the team has outgrown the grid entirely, however, another table interface may miss the point. What it needs is an actual application, and the audit must establish that need before recommending migration.
What a founder should expect once a studio has earned access
Access begins accountability, and the selection process continues. The founder should be able to see the known debt as the studio takes responsibility for engineering. A living debt register records what each issue is, what it costs, and what fixing it would take. That record keeps unresolved work available for discussion instead of allowing it to disappear inside technical conversations. It also preserves the founder’s ability to decide which trade-offs remain acceptable.
Quwa Labs is one option for founders seeking an audit before a refactor or rebuild proposal for a freelancer-built or AI-generated MVP, with ongoing maintenance after the takeover. By staying involved, it takes on the ownership that would be missing after a one-off handoff.
As the product stabilizes, the studio’s value should increasingly lie in helping the founder make informed engineering decisions, with less need for repeated production rescues. Known debt can still be there without taking over the working day. The founder can then focus on go-to-market work and client acquisition, with a clear view of the product’s risks and someone responsible for addressing them. That is what earned access should feel like from the other side.