How Engineering Studios Assess Your Stack Fitness Before Committing to a Roadmap
Engineering studios verify your codebase before promising delivery, not after.
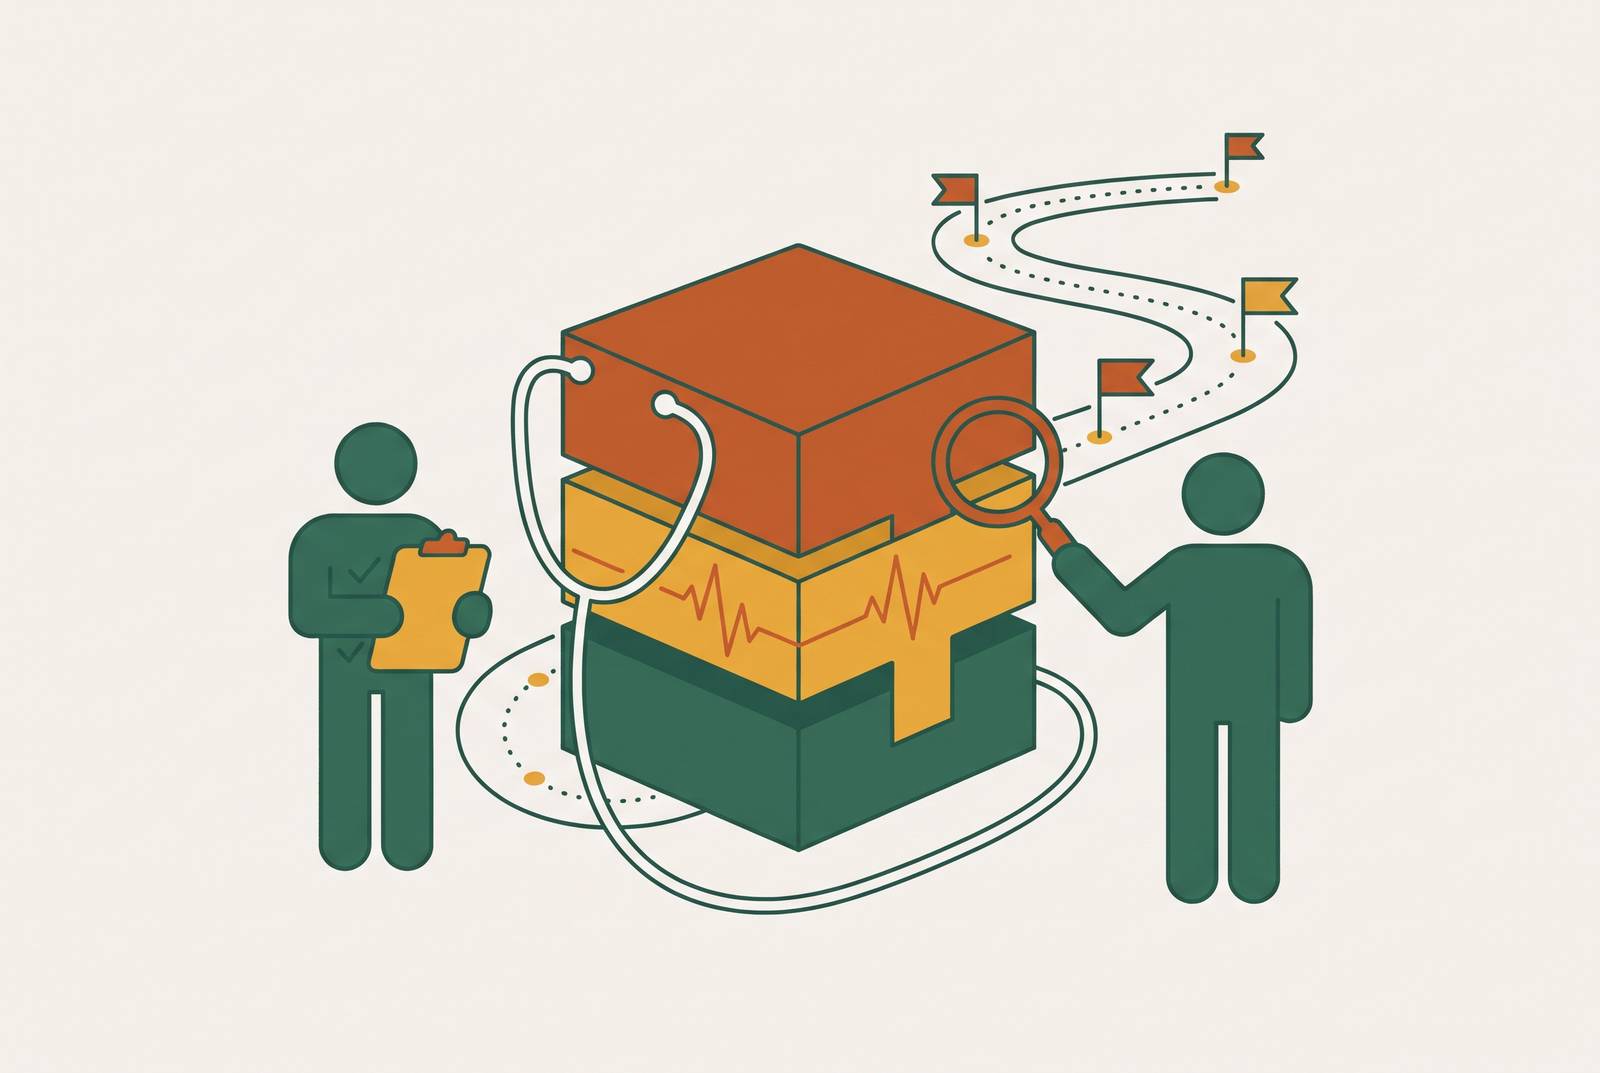
Before hiring an engineering partner, a technical debt assessment should independently examine the codebase, infrastructure, deployment pipeline, operational readiness, and distribution of team knowledge. Its output should be a scored register of risks and a prioritized plan. This is how engineering studios assess stack fitness before committing to a roadmap, making delivery promises depend on evidence.
Why studios refuse to commit to a roadmap before independently verifying the codebase
A founder may arrive with a working product, a backlog, and a launch date that already shapes business plans. Yet none of those tells a studio whether it can safely ship the next feature through the system as it stands. A demonstration proves less than a delivery commitment requires. Setting a price and schedule before checking what the work rests on means making promises before the constraints are known.
Those constraints often come to light only when the work begins. A plan can look sound during intake and unravel when changes encounter fragile dependencies, missing tests, or infrastructure that cannot support the intended load. The estimate assumes the system can accommodate work that nobody has independently assessed.
As working SaaS products become cheaper to build, that gap gets easier to miss. AI-built and no-code MVPs can reach users quickly without being designed for production load, security scrutiny, or handoff to another team. Moving toward production requires evidence beyond the fact that the MVP works.
What should a technical assessment cover before signing with a software development partner?
Context Studios uses an assessment framework with six dimensions, starting with architecture and code quality. This examines metrics, accumulated debt, and patterns that signal fragility under load. Security and compliance then covers OWASP coverage, secrets management, IAM configuration, and GDPR posture. These are separate tests of roadmap feasibility. A codebase can be readable while its access controls or handling of sensitive data still demand work before expansion.
Dependencies and supply chain form the third dimension, covering software composition analysis, a software bill of materials, license risk, and vendor maintenance status. DevOps and CI/CD form the fourth, examining pipeline maturity, test coverage, and parity between staging and production. A feature may be straightforward to write but difficult to test and release reliably through the current pipeline.
Cloud and costs looks at spending against what is actually used, including waste and chances for rightsizing that change what the budget needs to cover. Observability and operations asks whether monitoring is adequate, whether the system is ready for service-level objectives, and what happens when something breaks at 2 a.m. The review extends beyond the code itself. It must establish whether the organization can afford, release, and operate what the roadmap proposes.
The framework produces a scorecard with a value-versus-effort-and-risk heatmap, supply-chain analysis, architecture decision records, a cloud cost review, and a prioritized action plan. At the tool level, a scored register can organize findings around business value, technical health, and cost. Technical health includes vendor activity, project maintenance, runtime support, integration brittleness, and engineers’ willingness to be on call for the service. Finance can manage SaaS spending, but it cannot substitute for engineering judgment about architectural fit. A low bill does not establish that a dependency is safe to build around.
The behavioral signals that reveal debt no static analysis tool catches
Even a broad technical review can miss debt that has become normal to the team. How people behave around problems in the code often reveals debt. Are new features taking noticeably longer than six months ago despite the team staying the same size? Do engineers stay away from parts of the system because nobody fully understands their dependencies? Avoidance is evidence about the system, too.
A growing number of unrelated defects needs a different diagnosis from the same kind of bug coming back after repeated fixes. The latter suggests systemic fragility. Questions asked during a security review, SOC 2 process, or investor’s technical diligence can reveal a similar gap. If the team cannot answer confidently, the roadmap may depend on assurances the team cannot yet support.
Why distinguish ordinary cleanup from debt that supports the whole structure? Because debt under growth pressure can behave differently from debt at MVP scale. A slow database query that is barely noticeable with a small user base can bring down a site under heavy concurrent load. The risk does not necessarily rise gradually. Assessment has to consider the conditions under which an accepted weakness becomes a delivery blocker.
That is not a verdict on the founding team’s judgment. Skipping automated tests or choosing a simpler database schema can be reasonable ways to meet a launch date. Trouble develops when those trade-offs go untracked and deadline pressure never leaves room to revisit them. Debt is a predictable stage of growth. The task is to find which past compromises will no longer work in the next stage.
Team mapping exposes the human side of that task. Who owns each part of the system, where is knowledge concentrated, and what happens if one person leaves? Consider a feature that touches an area only one engineer understands. If that engineer is no longer available, the incoming team cannot count on learning the dependencies within the original estimate. The delivery risk lies in concentrated knowledge, even if static analysis finds nothing unusual.
Why discovery must be a formal gate, not a free pre-sales conversation
These questions require a process that makes candor possible. Free, unbounded discovery creates pressure for a studio to minimize risk to win the engagement, while a founder may downplay problems to avoid losing the partner. A formal gate changes the terms of that conversation. Its purpose is to establish what an engagement can responsibly promise.
WireApps describes discovery as a review of the codebase, infrastructure, team ownership, and backlog before committing to a delivery plan. The backlog review connects the technical findings to what is planned, what is already in flight, and what blocks other work. This sets out the evidence the studio needs before it agrees to delivery scope.
Giving discovery a set scope, sometimes for a fee, also gives it a clear endpoint. The deliverable identifies a starting point, explains why other areas remain outside the first phase, and separates quick wins from strategic initiatives. A founder can question a priority or a boundary instead of trying to interpret a vague warning that the system has concerns.
The strongest objection is understandable when capital is tight. Why pay for assessment and delay implementation when the product already needs work? The comparison is between a week of honest discovery and a five-week engagement that collapses when assumptions meet the actual system. For a studio that stays through implementation, discovery begins the partnership. Its findings become constraints that the same partner must work within.
How stack assessment changes when the client is a nonprofit
For a nonprofit, the review must account for obligations and resources that a purely technical lens can miss. The board remains accountable for the technology environment even when its members do not understand the systems inside it. Unknown compliance obligations can therefore create fiduciary as well as operational exposure. The codebase is only part of the picture. An assessment must also examine the organization’s ability to govern and sustain it.
Limited IT staffing, restricted revenue, and volunteer board governance narrow the available remediation paths. Regulated data environments involving HIPAA or donor PII add constraints that cannot be treated as optional backlog items. A technically sound change may still be a poor fit if the organization cannot support it. What can this team realistically maintain after implementation? That question belongs in the assessment before the roadmap is approved.
Tech Impact received a MacArthur Foundation grant in March 2026 to support digital and cybersecurity assessments for journalism and media organizations. The Agency Fund, collaborating with IDinsight, data.org, and Fast Forward, took a different approach by evaluating more than fifty AI tools to build a default nonprofit tech stack. That work drew on partnerships with nonprofits across Asia, Africa, and Latin America. For an engineering partner, nonprofit fit therefore means understanding governance, funding, and data obligations as constraints on the proposed work.
When assessment surfaces Airtable — and what an honest reassessment of that dependency looks like
Airtable illustrates how a reasonable early choice can grow into an unexamined production dependency. Teams often adopt it as a safe default, then expand the use case until it functions as an unofficial backend. The finding is that Airtable’s present role may demand something different from the role originally intended. Assessment has to identify that mismatch before proposing a migration.
If the core problem is a sync layer between a production database and Airtable, NocoDB can point directly at existing Postgres or MySQL instances, removing the need for that layer. NocoDB’s January 2026 change to a fair-code license also belongs in the dependency review. Licensing is part of stack fitness and must be assessed before selection.
If the requirement centers on GDPR, HIPAA, or SOC 2 compliance through self-hosted deployment, the assessment follows a different branch. Baserow holds GDPR, HIPAA, and SOC 2 Type II certifications applicable to its cloud and self-hosted deployments. To have full compliance controls on self-hosted instances, the organization needs a paid Advanced or Enterprise license. That qualification changes the scope of the decision. The deployment model and required controls must be assessed with their cost, rather than treating self-hosting alone as the answer.
If data volume is the breaking point, Teable is an AGPL-3.0 open-source Airtable alternative capable of handling million-row datasets. That makes it relevant to a capacity problem, while its suitability for each team using Airtable depends on that team’s requirements. These are different remedies for different findings. An honest assessment selects the branch that matches the constraint and scopes the resulting work, rather than turning one overstretched dependency into a mandate to rebuild everything.
What a roadmap built on verified stack fitness actually looks like — and why it commits differently
Once the constraints are explicit, the roadmap can connect technical work to business outcomes with a defensible baseline. Reducing system latency can be tied to customer satisfaction, while modernizing a data layer can be tied to enabling new revenue streams. Neither connection excuses vague technical scope. The roadmap names the starting point, explains the first phase’s boundaries, and distinguishes immediate improvements from longer strategic work.
Epics and technical milestones then account for existing debt. If a legacy service must be replaced before a new feature can ship, that dependency appears before the contract is signed. The sequence becomes part of the commitment. Business stakeholders can see why a prerequisite must come first before they learn halfway through delivery that it was needed.
A rolling update cadence of every two to four weeks keeps the roadmap responsive as implementation produces more information. The original assessment gives the team a grounded plan to revise as implementation produces more evidence. The partner who identified the constraints stays through implementation and remains responsible for working within them. That continuity gives the assessment practical value beyond the document.
For a founder who has reached product-market fit with an AI-built or no-code MVP, this is a transition toward growth. Users already depend on the product, so its foundations must improve without breaking what they rely on. Assessment gives that transition a workable sequence. Its return is the capacity to stop organizing the company around firefighting and begin executing on go-to-market plans with delivery commitments the engineering partner can stand behind.